The Great Re-Architecture
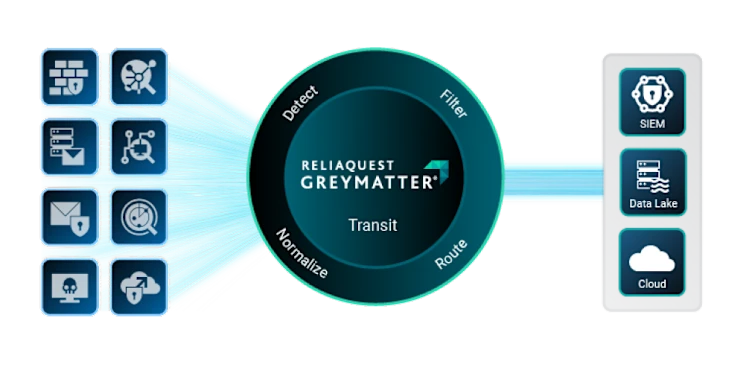
For years, the SIEM has been the most expensive, limiting part of security operations. Teams pay millions to ingest data, pay a premium to keep it searchable, and still wait hours on slow searches in the middle of investigations. Meanwhile, security data stopped living in one place—it's scattered across EDR, email, network, cloud, and OT, in multiple clouds and geographies—and AI-accelerated adversaries move faster than any ingest path can keep up with. That forces a tradeoff no team wants: centralize everything and watch the bill climb, or leave sources out and accept blind spots. GreyMatter Transit already moved detection out of the SIEM. But the SIEM still controls the two things it charges the most for: storing data and searching it.
That gap is why we built GreyMatter SIEM-Less: your team gets everything a SIEM does, without the SIEM. With data in low-cost object storage you own, it becomes searchable in seconds, and investigations, hunts, and reports all run in one native platform you already use for security operations.
What Is GreyMatter SIEM-Less?
GreyMatter SIEM-Less gives you all the benefits of the SIEM, without the tradeoffs. It indexes your security data as it lands in object storage you own. This allows queries, hunts, and investigations to return results in seconds, at a fraction of SIEM storage costs, with no per-query fees.
Key Features at a Glance
Search in Seconds
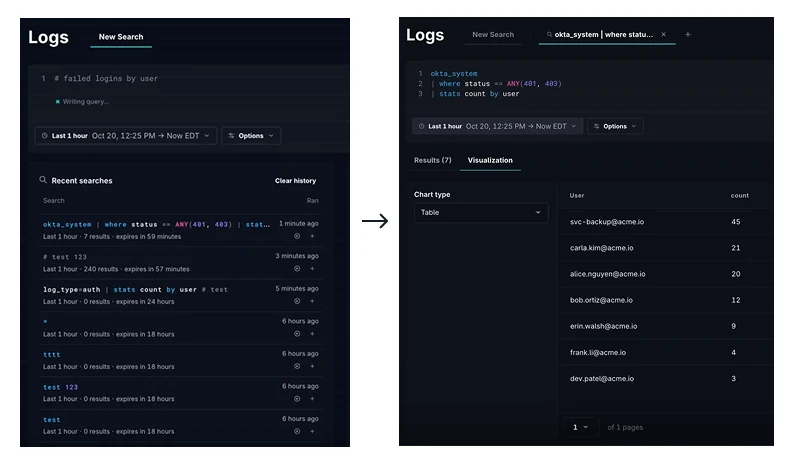
Ad hoc queries, threat hunts, and investigations return results almost instantly, cutting mean time to investigate from 20–25 minutes to under 5.
Decouple Detection from Storage
Data stays in object storage you own, which costs far less than SIEM storage. Keep what matters, drop what you don't need, and search as often as you want without paying per query.
Open Data You Own
Data is stored in an open format in storage you control. IT, compliance, and other teams can use it with their own tools, and it's never locked in a proprietary system.
The Full SOC Workflow in One Window
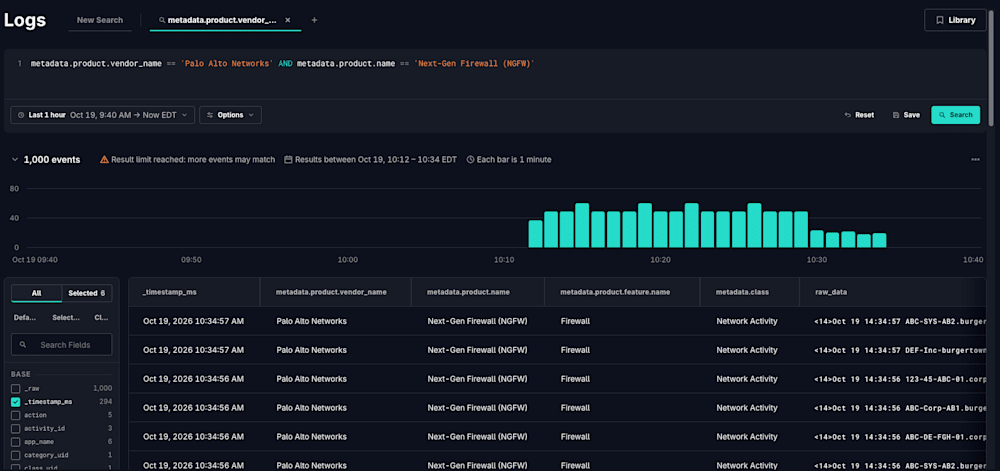
Search, hunting, investigation, response, saved searches, dashboards, and reporting all run in GreyMatter, in plain language or with structured queries.
Detect, Store, Search
Detect as data moves. Detections run in transit and at the source in under 60 seconds, before anything is stored.
Store what matters, where you choose. Noise is dropped. Everything else lands in object storage you own and is indexed as it's written, so it's ready to search right away.
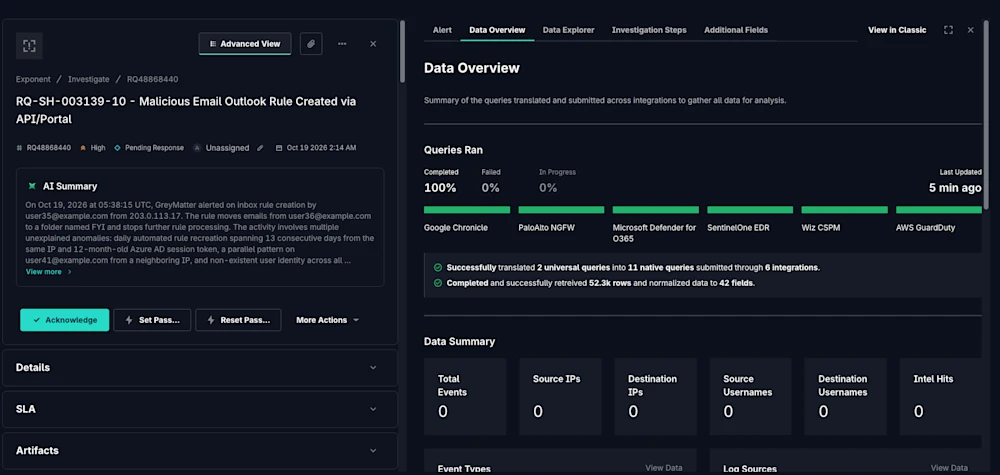
Search, hunt, and report from one place. Analysts run ad hoc queries, investigations, reports, and dashboards from GreyMatter. The IR Analyst Teammate investigates every alert, and the Threat Hunter Teammate runs long-term hunts across raw data. Containment happens from the same window.
Skip the Scan
When an analyst hunts for an IOC across months of firewall logs, SIEM-Less skips every file that can't contain a match and pulls back only the events that do. Most of the work happens when data is written, which is why searches that take minutes to hours in other tools come back in seconds. Results stream in as they're found, so analysts can start on the first hit right away.
Core Use Cases
Investigate faster: Mean time to investigate drops under 5 minutes—SOC analysts and the IR Analyst Teammate pull the context they need in seconds, so alerts get resolved while they still matter.
Hunt as often as you need: Threat hunters and the Threat Hunter Teammate search raw data whenever they want, with no per-query cost holding them back.
Look further back: Incident responders search older data to trace an attacker's earliest moves.
Retire the SIEM: Security leaders move search, investigation, and reporting into GreyMatter and keep retention in their own object storage, at a fraction of what SIEM storage costs.
Share one source of truth: IT, compliance, and data teams work from the same security data in its open format.
Why GreyMatter SIEM-Less Stands Apart
Predictable Where Query-in-Place Tools Aren't
Many tools that query object storage scan data at search time and charge for every byte scanned. On large hunts and repeated searches, those costs become prohibitive. SIEM-Less indexes data up front, so searches return in seconds and GreyMatter never charges per query.
Native to GreyMatter
Search, investigation, and response all run in the same platform you use for security operations, with no separate pipeline tool or search platform to connect.
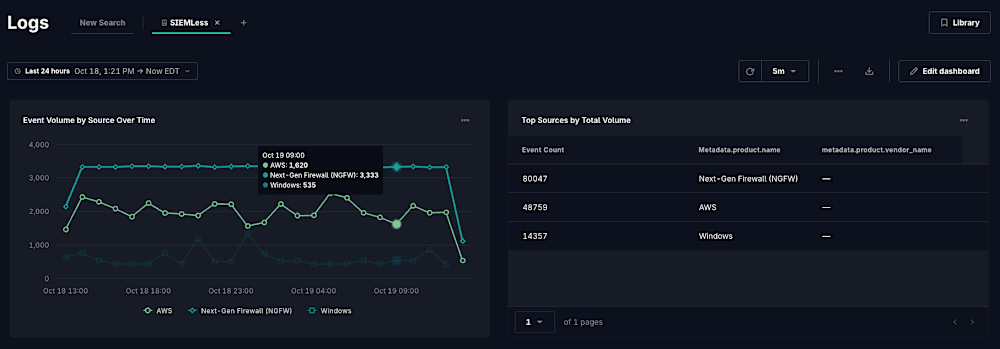
Faster than the SIEM. Data is indexed before anyone searches it, so ad hoc queries, hunts, investigations, and dashboards return results in seconds, with no waiting on a slow SIEM search layer.
Architectural Freedom. Detection is what usually locks an architecture in place—and running it at source or in transit removes that constraint. Plug new tools in, unplug them, and reshape the architecture as needs change, with retention in object storage you own. Because GreyMatter normalizes every field to the Open Cybersecurity Schema Framework (OCSF), swapping technologies never means rebuilding detections.
The Best ROI for the Enterprise. Data stays in object storage you own with no per-query fees from GreyMatter, so visibility grows without the cost compounding. Flat, predictable pricing prevents millions of dollars spent on unnecessary storage, ingestion, and query fees.
Search in Seconds with GreyMatter SIEM-Less
Request a demo to see how SIEM-Less turns object storage you own into fast, searchable security data, and to map out your move off the SIEM, including a plan for the data already in it.
The SIEM had a good run. Your data deserves a faster home.