A single puzzle piece never gives you the full picture. Its real value comes when it is connected to everything around it.
The same is true in security operations. A traditional SOC succeeds when people, processes, and technologies connect across the full threat lifecycle. An AI SOC must do the same. It needs to embed AI across every core SOC function to give teams the speed and visibility required for proactive defense.
However, not every platform claiming to be AI SOC is built to complete the picture.
Many “AI SOCs” are Point AI Tools in Disguise
Many platforms calling themselves an AI SOC are just point solutions that apply AI to a single, narrow function—AI for investigation and response, AI for detection engineering, AI for threat hunting, or AI for workflow automation. This creates significant operational gaps.
For example, an AI SOC tool might use AI to automate investigation and response after a phishing alert fires but does nothing to improve the detection that created the alert. Analysts are still forced to pivot between tools to understand whether the user clicked the link, entered credentials, or downloaded malware. AI speeds up one part of the triage, but the team is still stuck with gaps that attackers can use.
Another tool might apply AI to threat hunting to find malicious activity or lateral movement. But without AI-driven intelligence, the team still has to manually figure out what the activity means. As a result, the team has no actionable context to decide what to contain, monitor, or escalate.
While these isolated tools might improve a single step, the broader workflow remains fragmented, manual, and dependent on human handoffs. Security teams end up managing disconnected AI tools instead of operating a unified AI SOC.
To get the full value, security leaders need to know the difference between point solutions and a true AI SOC.
What Makes an AI SOC Truly Complete?
A complete AI SOC connects across the six core functions of security operations: investigation and response, detection engineering, threat hunting, threat intelligence, IT operations, and operational technology (OT).
When these pieces work together, security operations run as a single, unified system. AI carries context across the full threat lifecycle, eliminating manual handoffs and speeding up execution without adding cost or complexity.
With a complete AI SOC, your team gets:
Full AI capability: Agentic AI across every core SOC function, not just one workflow
Unified coverage: Visibility across the entire security operation, eliminating operational blind spots created by disconnected AI tools.
Seamless connectivity: Tool pivoting, manual handoffs, and fragmented workflows are eliminated so your team can move from detection to investigation to response faster.
Predictable cost: Cost controlled at the infrastructure level to avoid the volatility of token-based, query-based, or per-investigation pricing.
When adversaries are using AI to launch attacks in minutes, defense must use AI across the entire SOC to accelerate at the same speed. A complete AI SOC delivers the context and speed needed to respond faster and contain threats before they spread.
How GreyMatter Delivers The Most Complete AI SOC
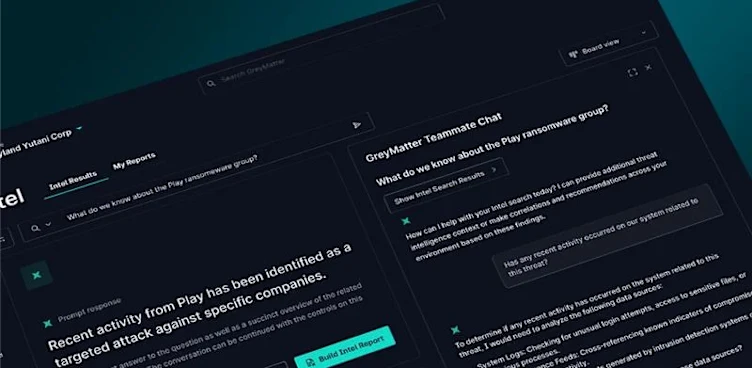
GreyMatter is the most complete AI SOC out, applying agentic AI across the entire security operations workflow and connected security stack, without creating another silo.
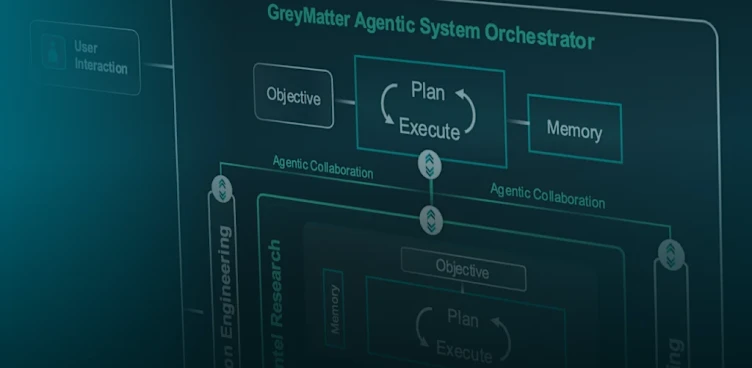
GreyMatter brings together six Agentic Teammates that cover the critical roles of the SOC. These role-based, autonomous agentic systems use 200+ agent skills and 400 AI tools to execute heavy operational work across IR, detection engineering, threat hunting, threat intelligence, IT, and OT.
Rather than acting like isolated task bots, the Agentic Teammates are coordinated through Agentic Orchestration, working together to perform multiple tasks at once and extend team impact. They function like senior teammates that understand your unique environment, recognize what matters, and work cross-functionally to guide defensive actions.
The measurable impact:
3X more output delivered by security teams
78M correlated alerts investigated annually
Less than 60 seconds to detect threats
Under 5 minutes to contain threats
Connect the Pieces, Complete the Picture
The true value of an AI SOC is measured when an attack is unfolding. When AI continuously carries context across every layer of the operation, the SOC transforms into a connected defense system built for scale.
As you evaluate AI SOC platform, ask yourself: “does it solve one piece of the puzzle, or does it connect the full picture?”