1. What is GreyMatter SIEM-Less?
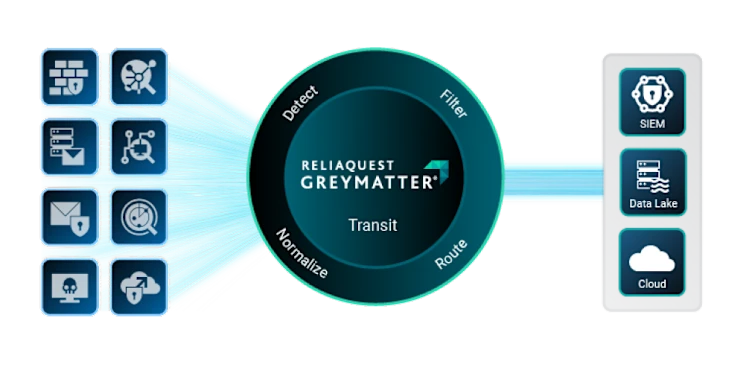
GreyMatter SIEM-Less is a capability of GreyMatter that gives security teams the benefits of a SIEM—including multi-event correlation, investigation and response, hunting, search, and reporting—without requiring a SIEM infrastructure. Data flows through GreyMatter Transit and is normalized to OCSF, detected in motion, and routed to customer's own object storage bucket. GreyMatter SIEM-Less makes that data easily searchable, while Agentic Teammates investigate and respond continuously. The result is faster detection, lower storage cost, broader visibility, and full security operations without relying on a traditional SIEM.
2. How does GreyMatter SIEM-Less detect threats without a SIEM?
GreyMatter uses its Transit capability to run single and multi-event detections as data moves from source technologies to storage, firing in seconds rather than waiting on ingest, parsing, and indexing. For technologies not going through Transit, detection runs at source. Triggered alerts are autonomously investigated by the IR Agentic Teammate, which enriches, reaches a disposition, and executes response actions.
3. How does SIEM-Less reduce costs compared to a traditional SIEM?
With SIEM-Less, high-volume data sources flow through Transit for detection first. Irrelevant telemetry can be filtered from the pipeline, while the remaining data is routed to lower-cost object storage that can be queried later through GreyMatter. GreyMatter handles the query and compute layer, so customers avoid the added costs of searching and processing that data in a traditional SIEM. Security teams get full detection coverage without paying to ingest every event, and they can bring detection to sources that were too expensive to centralize (OT, network telemetry, medical devices) without increasing your SIEM bill.
4. Can I still search and report on data with SIEM-Less?
Yes. Data stored in your object storage can be queried in natural language for ad-hoc investigations, threat hunting, saved searches, and compliance reporting from a single window in GreyMatter. You don't need a SIEM to search your data.
5. Does SIEM-Less mean I have to get rid of my SIEM?
No. SIEM-Less is about optionality, not replacement. You can route data to your existing SIEM, to object storage you own, or both. The point is that detection no longer depends on data landing in a SIEM first, so you control what gets stored, where, and how much based on your needs rather than your detection architecture forcing the decision.